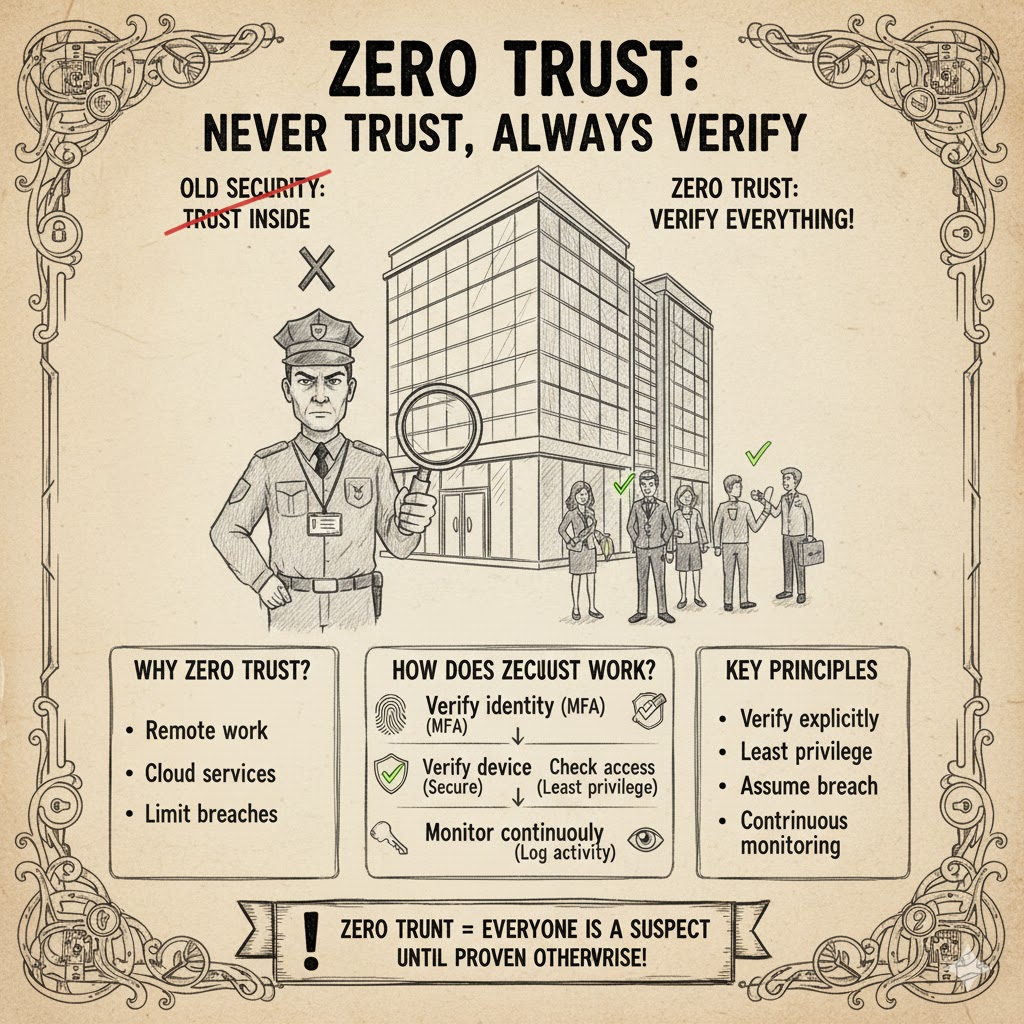
Zero Trust: Never Trust, Always Verify
Zero Trust is a modern security approach that says "Never automatically trust anyone or anything — always check!" It's like having security guards check everyone's ID, even people who work in the building every day!
What is Zero Trust?
Old security ("castle and moat") assumed the inside was safe. Zero Trust says: don't trust by default — verify every access request, every time.
Why Zero Trust?
- Remote work and cloud services break the old perimeter model
- If attackers get inside, they shouldn't be able to roam freely
- Zero Trust enforces continuous verification and least privilege
How does Zero Trust work?
- Verify identity: Multi-factor authentication (password + phone code, etc.)
- Verify device: Is the device secure and compliant?
- Check access: Does the user need this resource (least privilege)?
- Monitor continuously: Log and analyze behavior; block anomalies
Key principles
- Verify explicitly — Authenticate and authorize every request
- Least privilege — Grant only the access needed
- Assume breach — Design as if attackers are already inside
- Continuous monitoring — Inspect and log all activity
Technologies often used
- Multi-Factor Authentication (MFA)
- Micro-segmentation
- Identity and Access Management (IAM)
- Encryption everywhere
- Behavior analytics / continuous monitoring
Example (remote work)
Sarah works from home. Under Zero Trust she must authenticate with MFA, the device is checked, access is limited to what she needs, and unusual downloads trigger alerts — so a stolen password alone is not enough for an attacker to cause damage.
問題1: Zero Trust(ゼロトラスト)は、「誰も自動的に信頼せず、常に検証する」というセキュリティアプローチである。
問題2: Zero Trustでは、一度ログインすればその後は検証が不要である。
問題3: Zero Trustの原則には、必要最小限の権限(Least Privilege)を与えることが含まれる。
問題4: Zero Trustの考え方の一つに「侵入を前提とする(Assume breach)」がある。
問題5: Zero Trustは、クラウドやリモートワークが増えた現代に適したセキュリティアプローチである。


