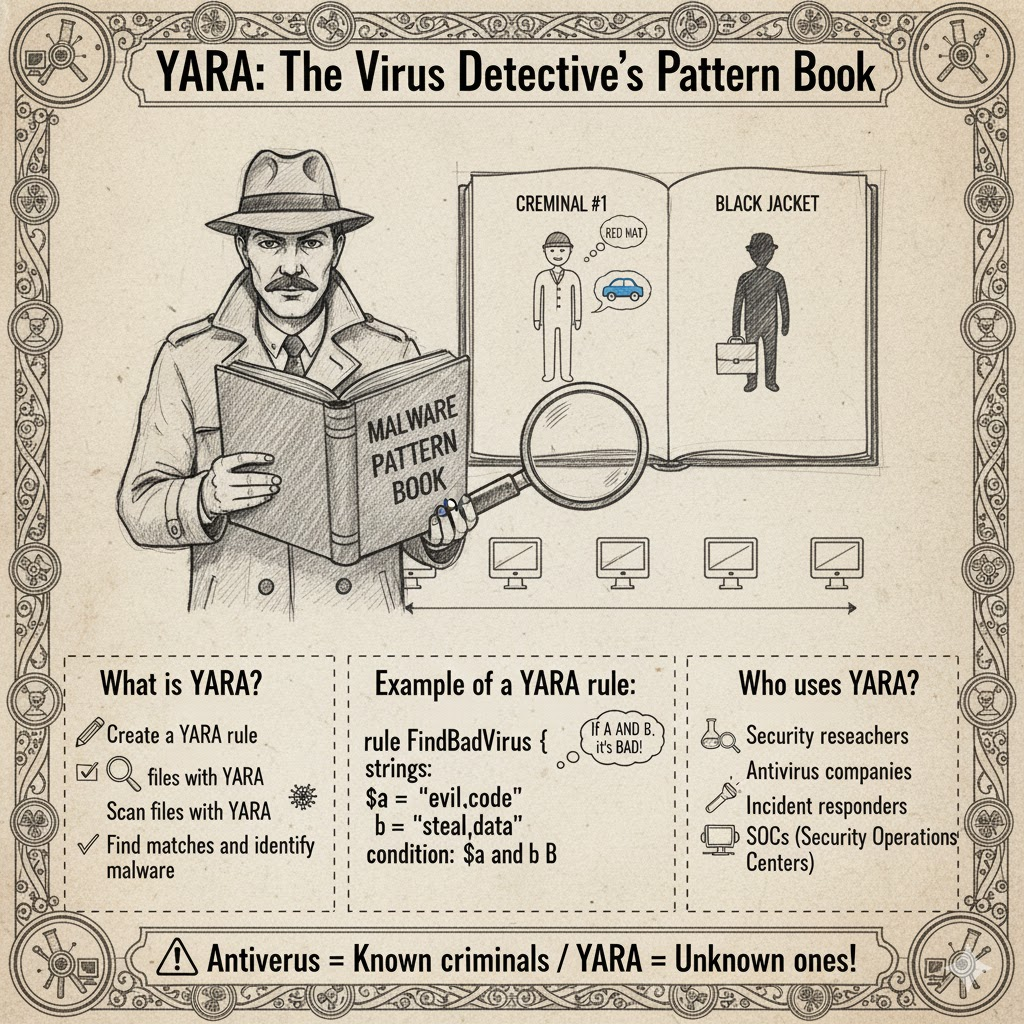
YARA: The Virus Detective's Pattern Book
YARA is a special tool that helps security experts find and identify malware (bad software). It's like a detective's notebook that describes what different criminals look like!
What is YARA?
Imagine you're a police detective looking for bad guys. You have descriptions:
- "Criminal #1: Tall, red hat, drives a blue car"
- "Criminal #2: Short, black jacket, carries a briefcase"
- "Criminal #3: Wears sunglasses, has a scar on left hand"
When you see someone matching a description, you know "That's the criminal!"
YARA works the same way for finding malware! Security experts write "rules" that describe what malware looks like, and YARA searches computers to find matches.
How does YARA work?
- Create a YARA rule describing malware characteristics
- Scan files with YARA
- Find matches and identify malware
- Take action: quarantine, delete, or investigate
Example of a YARA rule:
rule FindBadVirus {

    strings:

        $a = "evil_code"

        $b = "steal_data"

    condition:

        $a and $b

}
This means: "If a file contains both 'evil_code' AND 'steal_data', it's probably bad!"
Who uses YARA?
- Security researchers – analyze new malware and create detection rules
- Antivirus companies – integrate YARA into their products
- Incident responders – hunt for malware after attacks
- SOCs (Security Operations Centers) – monitor and detect threats
Why is YARA important?
- Fast detection: Scans thousands of files quickly
- Flexible: Customizable rules for new threats
- Community sharing: Experts share rules globally
- Proactive hunting: Actively search for threats
YARA vs Traditional Antivirus
| Traditional Antivirus | YARA |
|---|---|
| Has a database of known viruses | Uses custom rules |
| Automatic for normal users | Manual, for experts |
| Detects known threats | Finds new or hidden threats |
Analogy:
Antivirus = Security guard with a list of known criminals
YARA = Detective writing new descriptions to catch unknown ones
YARA is open source! Anyone can use and contribute to improve malware detection worldwide.
問題1: YARA(ヤラ)は、マルウェアを検出・識別するためのパターンマッチングツールである。
問題2: YARAは、一般のコンピュータユーザーが日常的に使う簡単なツールである。
問題3: セキュリティ専門家は、YARAルールを作成してマルウェアの特徴を記述できる。
問題4: YARAルールは、世界中のセキュリティコミュニティで共有されている。
問題5: YARAは、従来のウイルス対策ソフトと全く同じ機能を持っている。


