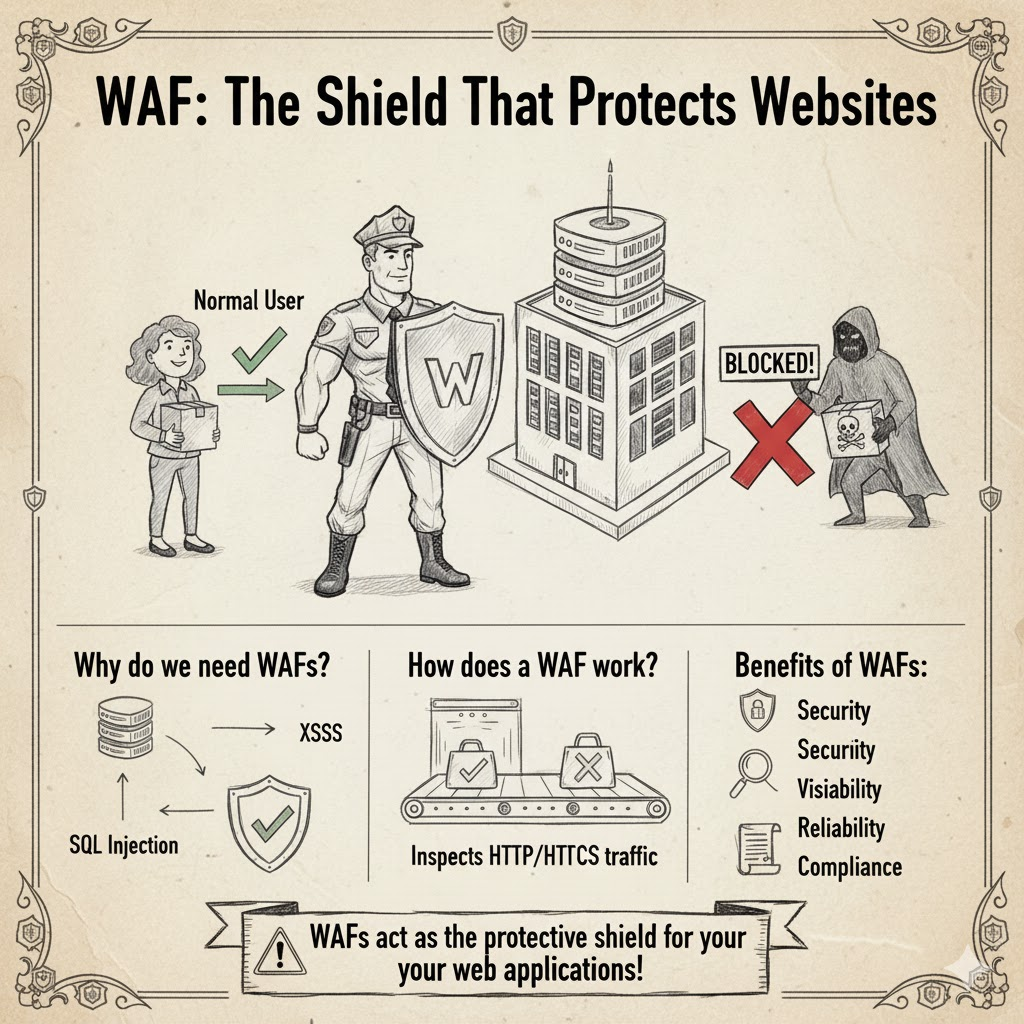
WAF: The Shield That Protects Websites
WAF stands for "Web Application Firewall."
It’s like a **security guard** standing in front of your website, checking all visitors before they enter!
What is a WAF?
Imagine a large office building with many visitors coming in and out every day:
- Some visitors are employees (normal users)
- Some are guests (new visitors)
- But some might try to sneak in and cause trouble (attackers!)
A WAF works like the security guard at the entrance — it checks who’s coming in and what they’re carrying before letting them inside your web server.
Why do we need WAFs?
Without a WAF, attackers can send harmful data to your website — like SQL Injection or Cross-Site Scripting (XSS) attacks.
With a WAF:
- Suspicious requests are blocked automatically
- Normal users can access safely
- Attackers are stopped before reaching your system
How does a WAF work?
Think of it like an airport security check:
- Without WAF: Anyone can walk in without inspection → Danger!
- With WAF: Every bag (request) is scanned → Only safe ones pass!
WAFs inspect **HTTP and HTTPS traffic** and decide whether to allow, block, or log each request.
Real-world example:
An online shopping site might use WAFs like this:
- Block attacks that try to steal customer data
- Filter out bots sending fake orders
- Prevent unauthorized access to admin pages
Even if attackers know your website’s address, the WAF stands between them and your system!
Benefits of WAFs:
- Security: Protects against common web attacks (SQL Injection, XSS, etc.)
- Visibility: Logs suspicious behavior for later analysis
- Reliability: Keeps services running even under attack
- Compliance: Helps meet security standards (like PCI DSS)
Key Point: WAFs act as the **protective shield** for your web applications — stopping attacks before they reach your system.
問題1: WAFは、Webアプリケーションを攻撃から守るファイアウォールである。
問題2: WAFは、ネットワーク全体の通信を監視することを目的としている。
問題3: WAFは、SQLインジェクションやXSSのような攻撃を防ぐことができる。
問題4: WAFは、Webサーバとインターネットの間に配置される。
問題5: WAFを導入すれば、すべての攻撃を100%防げる。


